
As organizations increase WAN capacity, connect more locations, and move larger volumes of traffic through the network edge, the firewall infrastructure can take on a substantially heavier role.
At headquarters or in a data centre, it may be terminating VPN connections from several sites while simultaneously handling Internet traffic and enforcing security policy between high-speed networks. At that point, the requirements extend beyond simply finding a firewall capable of supporting the available Internet bandwidth.
The Netgate 8300 with pfSense Plus is built for these higher-capacity environments, particularly where the network edge needs to handle multi-gigabit firewall traffic, substantial VPN workloads and integration with enterprise or data-centre infrastructure.
When the Network Edge Needs More Capacity
Consider an organization with several branches connected back to headquarters.
Each individual branch may generate a manageable amount of traffic, but the headquarters firewall sees the combined workload. Business applications, Internet access, and encrypted traffic from remote locations can all converge at the same point.
The same situation can occur without a large branch network. An organization moving from 1 Gbps connectivity to several gigabits may find that the firewall becomes the limiting component between its WAN and internal infrastructure.
The Netgate 8300 firewall provides significantly more processing capacity for these environments. Netgate currently publishes performance of up to 28.6 Gbps firewall throughput and 14.6 Gbps IPsec VPN throughput under its stated iPerf3 test conditions. Actual performance will depend on packet sizes, configuration, and the services being run, but those figures position the appliance well above conventional branch-firewall workloads.
For a customer evaluating the 8300, the more useful question is therefore not simply:
How fast is our Internet connection?
It is:
How much network traffic will converge on this firewall, and what will it be expected to do with that traffic?
That distinction becomes especially important when VPN forms a significant part of the workload.
A Better Fit for High-Speed Enterprise Network Infrastructure
The Netgate 8300 enterprise firewall also makes sense when the surrounding network has moved beyond ordinary Gigabit Ethernet.
It provides four 10 GbE SFP+ interfaces alongside 1 GbE SFP and 2.5 GbE RJ45 connectivity. Netgate also offers optional 25G and 100G network interfaces through the platform's expansion capability.
That opens up deployments where the firewall needs to connect directly into a 10 GbE core, terminate higher-speed WAN services, or sit between several high-capacity network segments.
A typical enterprise deployment might have a 10 GbE connection toward the core switching infrastructure, separate WAN connectivity and multiple VPNs terminating on the same appliance. In that environment, choosing a firewall based only on the Internet circuit would ignore much of the traffic the appliance is actually expected to process.
The physical design of the Netgate 8300 also reflects that role. It is a 1U rack-mounted platform, and the MAX configuration includes dual hot-swappable power supplies. Netgate also supports the 8300 in pfSense Plus High Availability pairs.
Those capabilities matter more when the firewall is supporting infrastructure that the business cannot easily take offline for maintenance or hardware failure.
Where the 8300 Fits in the Netgate Firewall Portfolio
The Netgate 8300 should not simply be treated as the next Netgate model in numerical order.
Platforms such as the 4200, 6100 and 8200 remain well suited to many branch, SMB and enterprise-edge deployments. Netgate itself positions the 8300 for environments extending into large business networks, with 10 GbE connectivity and rack-mounted deployment.
The Netgate 8300 becomes more compelling as several higher-end enterprise firewall requirements begin to appear in the same project.
A business may need considerably more VPN capacity because headquarters terminates connections from many remote locations. The network may already operate at 10 GbE internally. Additional interface capacity or future expansion may also be part of the design. Resiliency requirements may call for redundant power or an HA pair.
These requirements change the nature of the firewall project.
The decision is no longer simply between different throughput numbers, but a question of which platform belongs at the centre of the network architecture being built.
That is also why replacing an existing firewall with an 8300 should not be treated as a straightforward hardware upgrade. The opportunity should be used to review how WAN services, VPN connectivity and the surrounding network infrastructure interact with the firewall.
Positioning the Netgate 8300 Around the Requirement
The value of the Netgate 8300 is not in selling the largest appliance available.
The opportunity is identifying the environments where its additional capacity and infrastructure features solve a real network requirement.
An enterprise headquarters consolidating VPN connectivity from multiple branches presents one case. A data-centre edge connected to 10 GbE switching presents another. An organization increasing WAN capacity while retaining pfSense Plus as its firewall platform may also reach a point where the 8300 becomes the appropriate step up.
As an Authorized Netgate Value-Added Reseller, Optace Networks can assess those requirements before the platform is selected, then supply and integrate the 8300 into the wider network design.
That includes determining whether the workload warrants the Netgate 8300, how its interfaces should connect to the existing infrastructure, and whether the deployment should incorporate options such as redundant power or a high-availability pair.
The objective is not simply to put a more powerful firewall at the edge, but to deploy a platform with the capacity and connectivity to support the network around it.
If your organization is evaluating higher-capacity firewall or VPN infrastructure, Optace Networks can help determine whether the Netgate 8300 is the right fit and design the pfSense Plus deployment around the actual network requirements
Latest Articles
Wed Oct 14 2026
Netgate 8300 for High-Capacity Firewall and VPN DeploymentsFri Sep 18 2026
How to Size a Netgate Firewall for Your Business NetworkWed Sep 09 2026
Planning Internet Failover with Netgate and pfSense PlusFri Aug 28 2026
Fuzion FTP-300 for Outdoor IoT and Surveillance NetworksRelated Articles

ePMP 3000 - 5X Performance with Gen3 Technology

Africa Tech Festival Displays Strides in Connectivity and Telecommunications Infrastructure across Africa
Cambium Networks ePMP Force 425 - The Industry’s First Point-to-Point Solution Based on 802.11ax
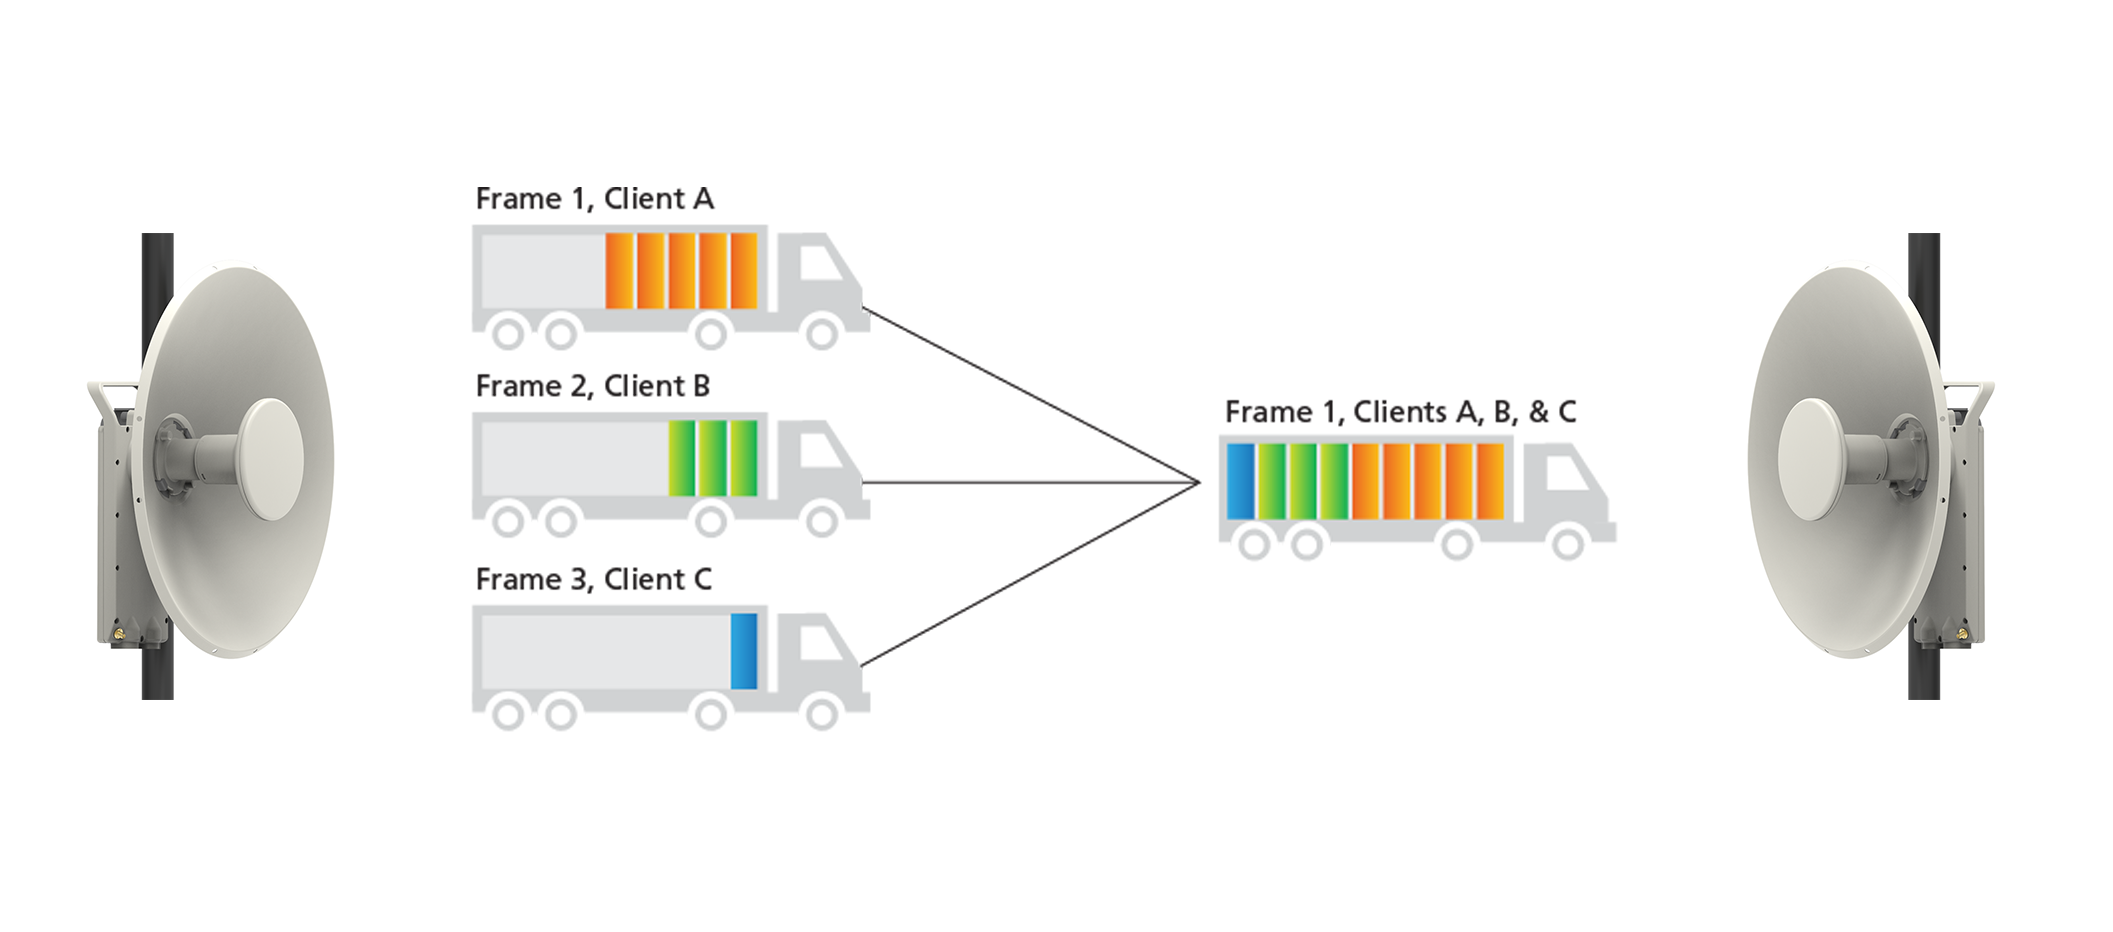
The Power of OFDMA in Wireless Broadband
In this article, we delve into the principles of OFDMA, the defining principle of the 802.11ax standard, its applications, and its impact on wireless broadband.


© 2026 PoweredbyOptace Networks Limited. All Rights Reserved.